
Tech Deep Dives & Demos | Czech Sausage Buffet & Beers
AI-Powered Pentesting, Vulnerability Management & Infrastructure Security
December 10, 2026 @ Helsinki, Finland
Patching, Pentesting & Pils
In this technical session we will be exploring AI-powered penetration testing, attack surface management, automated patching, container security, and Kubernetes observability.
The focus is on real-world scenarios, technical insights, and live demos, exploring how attackers discover and exploit vulnerabilities – and how organizations can effectively identify, prioritize, and address these risks.

Czech-style sausage buffet & beers
We’ll round off the event with a Czech-style sausage buffet, a selection of Czech beers, and plenty of time for networking. Other drinks will be available too, of course!
Welcome!
This event is designed for technical professionals working in cybersecurity, Linux administration, Kubernetes, DevOps, platform engineering, and IT infrastructure.
Agenda
Thursday, December 10, 2026
14:30
Doors open
Coffee & refreshments available
15:00
Welcome & Kickoff
15:05
The Attacker’s Perspective – AI-Powered Pentesting & Exposure Validation
How can AI agents discover and test vulnerabilities from an attacker’s perspective? We’ll explore continuous external attack surface discovery, automated penetration testing, and the validation of real-world exploitability. Technical presentation & live demo.
/ Stirling Fisher, Solutions Architect, Hadrian
15:50
Break
16:00
The Defender’s Perspective – Patching, Container Security & Observability
How can organizations efficiently remediate vulnerabilities, protect containerized workloads, and maintain visibility across complex Kubernetes environments? We’ll explore automated security patching, container runtime protection, and Kubernetes observability, including practical approaches to vulnerability remediation, threat detection, and troubleshooting. Technical presentation & live demo.
/ Olli Tuominen, Solutions Architect, SUSE
16:45
Break
16:55
Closing the Loop – From Exploitable Vulnerabilities to Verified Remediation
What happens after a vulnerability has been discovered? How can we prioritize remediation, verify that fixes are effective, and reduce the risk of future exploitation? In this session we’ll bring together the attacker’s and defender’s perspectives, examining how vulnerability discovery, remediation, and validation can work together in practice.
/ Stirling Fisher, Solutions Architect, Hadrian
/ Olli Tuominen, Solutions Architect, SUSE
17:45
Czech Dinner & Networking with other participants
Slow-cooked pork shank, bratwurst and wild boar beer sausage, creamy pepper sauce and house mustard. Also horseradish sauerkraut braised in smetana, roasted herb potatoes and seasonal vegetables.
20:00
Event ends
Program subject to modifications
Location
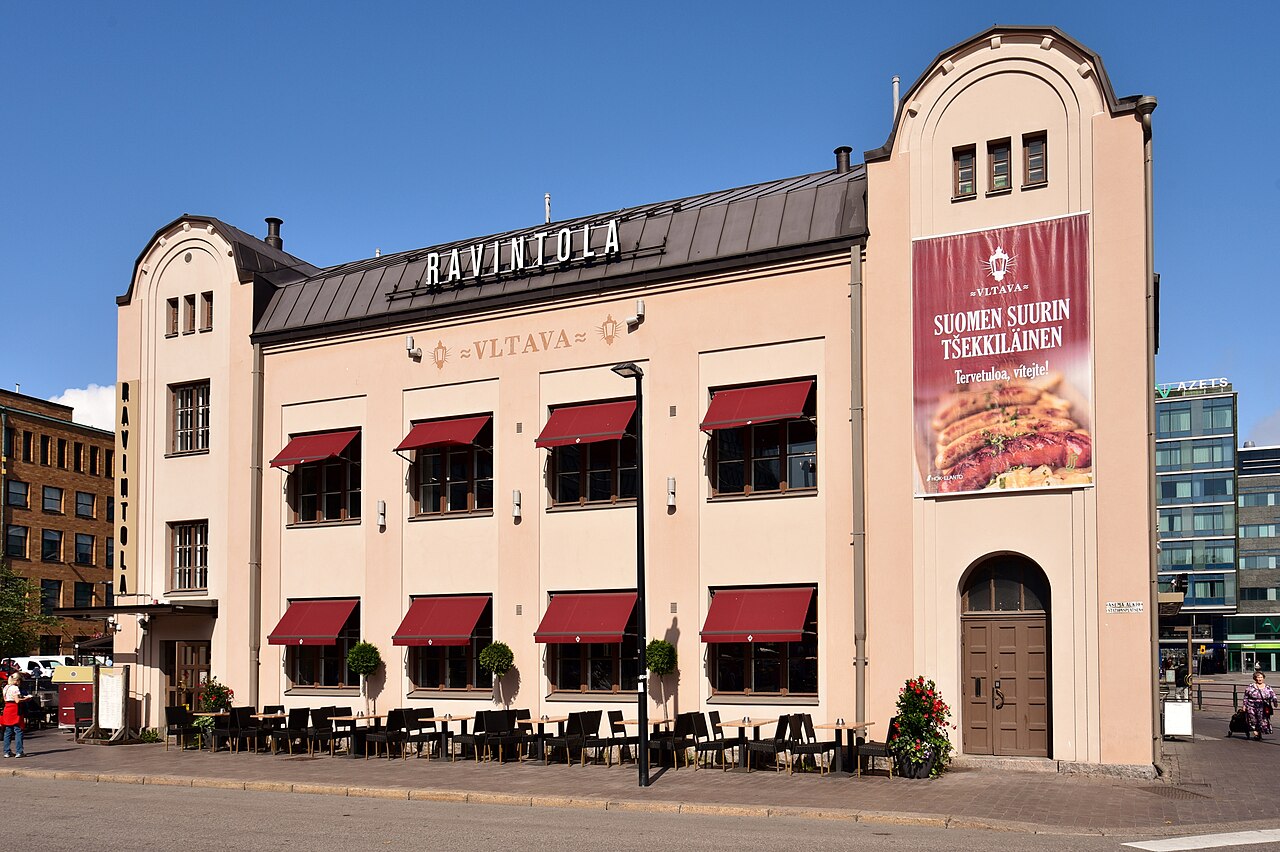
Restaurant Vltava / Havel room
Elielinaukio 2, Helsinki
Finland
In cooperation with:


Session Specialists
Stirling Fischer
Solutions Architect,
Hadrian
Olli Tuominen
Solutions Architect,
SUSE
Michael Svendsen,
Head of Pre-Sales and Services,
Nordicmind
Registration
Note: In case the form says the event is full, kindly register for the waiting list. Most likely there will be more seats available. We will be in touch with you!
By registering you agree with Nordicmind’s Privacy Policy
The event is organized by Nordicmind. For any questions and inquiries kindly contact events[at]nordicmind.com